Articles in this section
User Management - Profiles
Feature Availability
Vtiger Editions: One Pilot | One Growth | One Professional | One Enterprise | One AI
Introduction
A CRM profile defines what actions a user can perform on CRM records. You can create different profiles, such as Sales, Support, and Marketing. When a profile is associated with a role, the access rights defined in the profile apply to all users with that role.
Note:
- By default, only Admin users can set up Profiles for other users.
- Users represent your employees who can sign in to the CRM and use its features.
- For example, Jenny, a Sales Manager, and Mark, a Support Executive, have their own logins.
- Roles define a user's position in your organization's hierarchy.
- For example, Jenny is assigned the Sales Manager role, while Alex reports to Jenny as a Sales Representative.
- Profiles determine the modules, fields, and actions a user can access.
- For example, a Sales profile is created, providing access to all the features in the Sales app.
- Groups allow multiple users to collaborate and share ownership of records.
- For example, a Sales group is created with the sales team as members.
- Sharing Rules extend record access beyond the role hierarchy when collaboration across teams is required.
- Visibility Settings control who can view, edit, delete or share records across the organization.
- For example, a Sales Representative can create and edit Leads but cannot access CRM Settings, whereas a Sales Manager with Admin user type can access all modules and settings.
Benefits
The benefits of using the Profiles feature are that it:
- Controls what users can view, create, edit, and delete across CRM modules.
- Protects sensitive business data with field-level access control.
- Simplifies user permission management by assigning permissions through roles.
- Ensures that users access only information relevant to their responsibilities.
- Reduces the risk of unauthorized changes or accidental data deletion.
- Standardizes permissions for teams with similar job functions.
- Supports secure collaboration across Sales, Support, Marketing, and other teams.
In this article, you will learn about managing User Profiles.
Creating a Profile
Creating a profile is simple, but that alone is not enough. To apply a profile's permissions to a user, you must associate a role with the profile. Then, users having the associated role will have the permissions set for the profile.
So, here are the four steps that you must perform to complete the setup.
Step 1: Creating a profile
- Log in to the CRM.
- Click the User Menu in the top right corner of the CRM screen.
- Click Settings.
- Look for the User Management section.
- Select Profiles.
- Click the +Add Profile button.
- Enter the profile name and description.
Step 2: Defining permissions
- Go to the Edit privileges section for this profile.
- Choose an app (Inventory, Sales, etc.) from the Edit privileges section of the profile, then click the downward arrow.
- Choose a module. Enable or disable the View, Create, Edit, or Delete checkboxes to grant or revoke the corresponding permissions for the module.
- Click the downward arrow on a module. All the fields in the module are shown in the Fields section.
- Move the toggle button beside a field to the left to make it invisible, to the center to make it read-only, or to the right to make it writable. Black colour represents invisible, Orange represents read-only, and Green represents writable. Note: You cannot change permissions for mandatory fields.
- Scroll down to the Tools section. Enable the checkbox to provide access to a tool. Disable it otherwise.
- Click Save.
Step 3: Linking a role with a profile
- Click the User Menu in the top-right corner of the screen.
- Click Settings.
- Look for the User Management section.
- Select Roles.
- Click on a role to edit it.
- Select Assign privileges from existing profiles under Privileges.
- Select the profiles under Assign Profiles.
- Click Save.
Step 4: Assigning the role to users
- Click the User Menu in the top right corner of the CRM screen.
- Click Settings.
- Look for the User Management section.
- Select Users.
- Open a user record to set the role.
- Click the Edit icon on the top right side.
- Look for the Roles field.
- Select a role.
- Click Save.
To learn more about Users, click here.
To learn more about Roles, click here.
Profile permissions are divided into two parts:
- Module permissions
- Permissions on fields and tools
Module Permissions
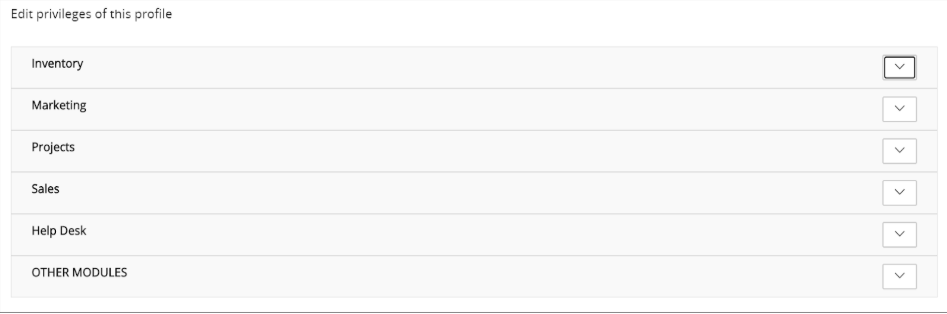
- When you open a profile, you see the following. Inventory, Marketing, Projects, etc., are all apps.
)
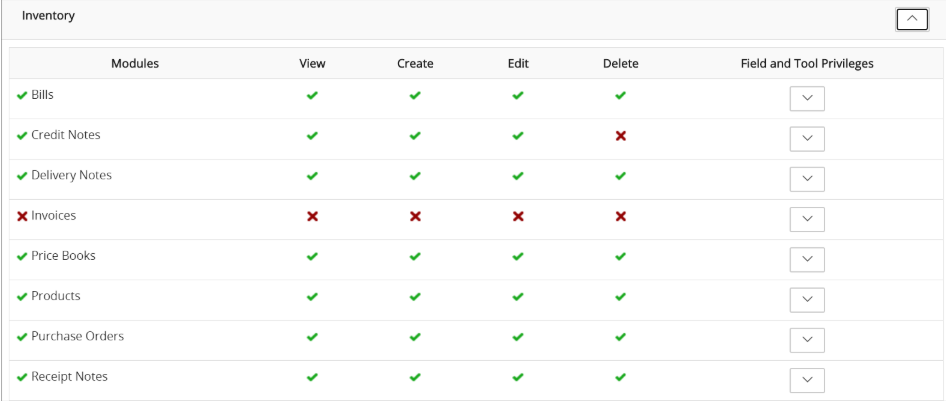
- Each app has multiple modules. When you click the downward arrow on the right side, you will see the modules.
- When you click the Edit icon in the top-right corner of the page, you can edit module permissions.
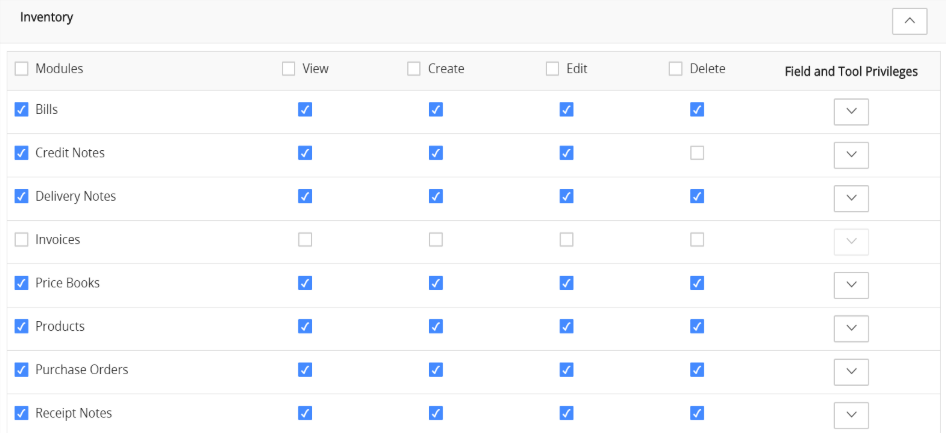
- Enable a checkbox to provide the permission mentioned in the column name.
- Enable the Modules checkbox to provide all permissions on all modules.
- Enable the checkbox next to a module name to grant all permissions for the module.
- Enable the checkbox next to View, Create, Edit, or Delete to grant the corresponding permission across all modules.
Permissions on fields and tools
As a CRM admin, you can decide who can view and edit field values. Also, you can allow or deny access to tools such as import, export, and duplicate handling in the modules.
Centre, Orange = Field is read-only
Right, Green = Field is writable (editable)
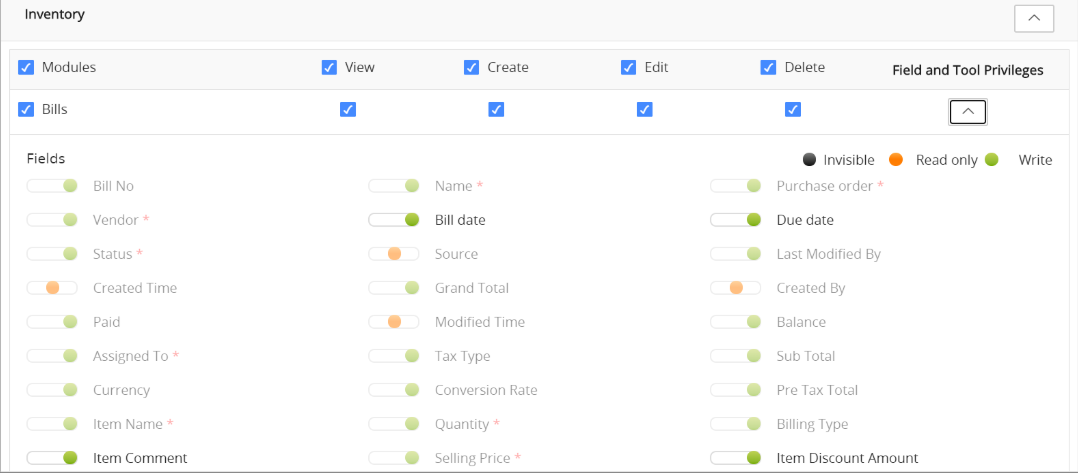
- In addition, you will also see tools relevant to the module by scrolling down. Enable or disable the checkbox beside a tool to control its permissions
- Do not forget to click Save after you make changes to profile permissions.
Note:
- If the Override From Email ID checkbox under the Cases > Tools is enabled, CRM users, agents, and others can change the From email ID when replying to a Case.
- Users can choose the email ID only if multiple IDs have been configured for the Help desk.
- If this field is disabled, users cannot change the From email ID.
Deleting a Profile
When you delete a profile, you must transfer the roles belonging to the profile (being deleted) to another profile.
Follow these steps to delete a profile:
- Log in to the CRM.
- Click the User Menu in the top right corner of the CRM screen.
- Click Settings.
- Look for the User Management section.
- Select Profiles.
- Hover over a profile.
- Click the Delete icon.
- Select a profile to transfer ownership from the Transfer roles to profile drop-down.
- Click Save.
Profiles vs. Sharing Rules
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
Note: Sharing Rules, Profiles, and Roles pages now display information regarding Sharing Rules, Profiles, and Roles, making it easier for you to distinguish each of them.
To learn more about sharing rules, click here.
Note:
- You can associate multiple users and profiles with the same role.
- When you associate multiple users with the same role, those users cannot see one another’s records in a module if the module's sharing rules are set to Private.
- A role always works with respect to Profiles and Sharing Rules.
- Sales Insights and Help Desk Insights do not follow ‘Field-level restrictions’ in a profile. Even if fields such as Amount, Sales Stages, etc., are restricted in Profiles, users who are given access permission to Sales Insights and Help Desk Insights can view these fields.